Stop burning RDP persistence with 4732 alerts. Bypass the "Remote Desktop Users" group entirely .......
- 573 likes
- 5 comments
- 117 reposts
International joker who is occasionally heroic behind the keyboard.
I'm a security researcher. I spend my working hours inside networks that would rather I weren't: simulating the adversaries a company is actually likely to meet, taking apart Active Directory, and getting payloads past controls built to stop exactly that.
Everything I learn gets written down. Raw notes land in the vault the moment I find something. Finished research and lab writeups go to the blog. The work worth putting in front of the wider Arab security scene goes to Red Team Recipes.
Certifications
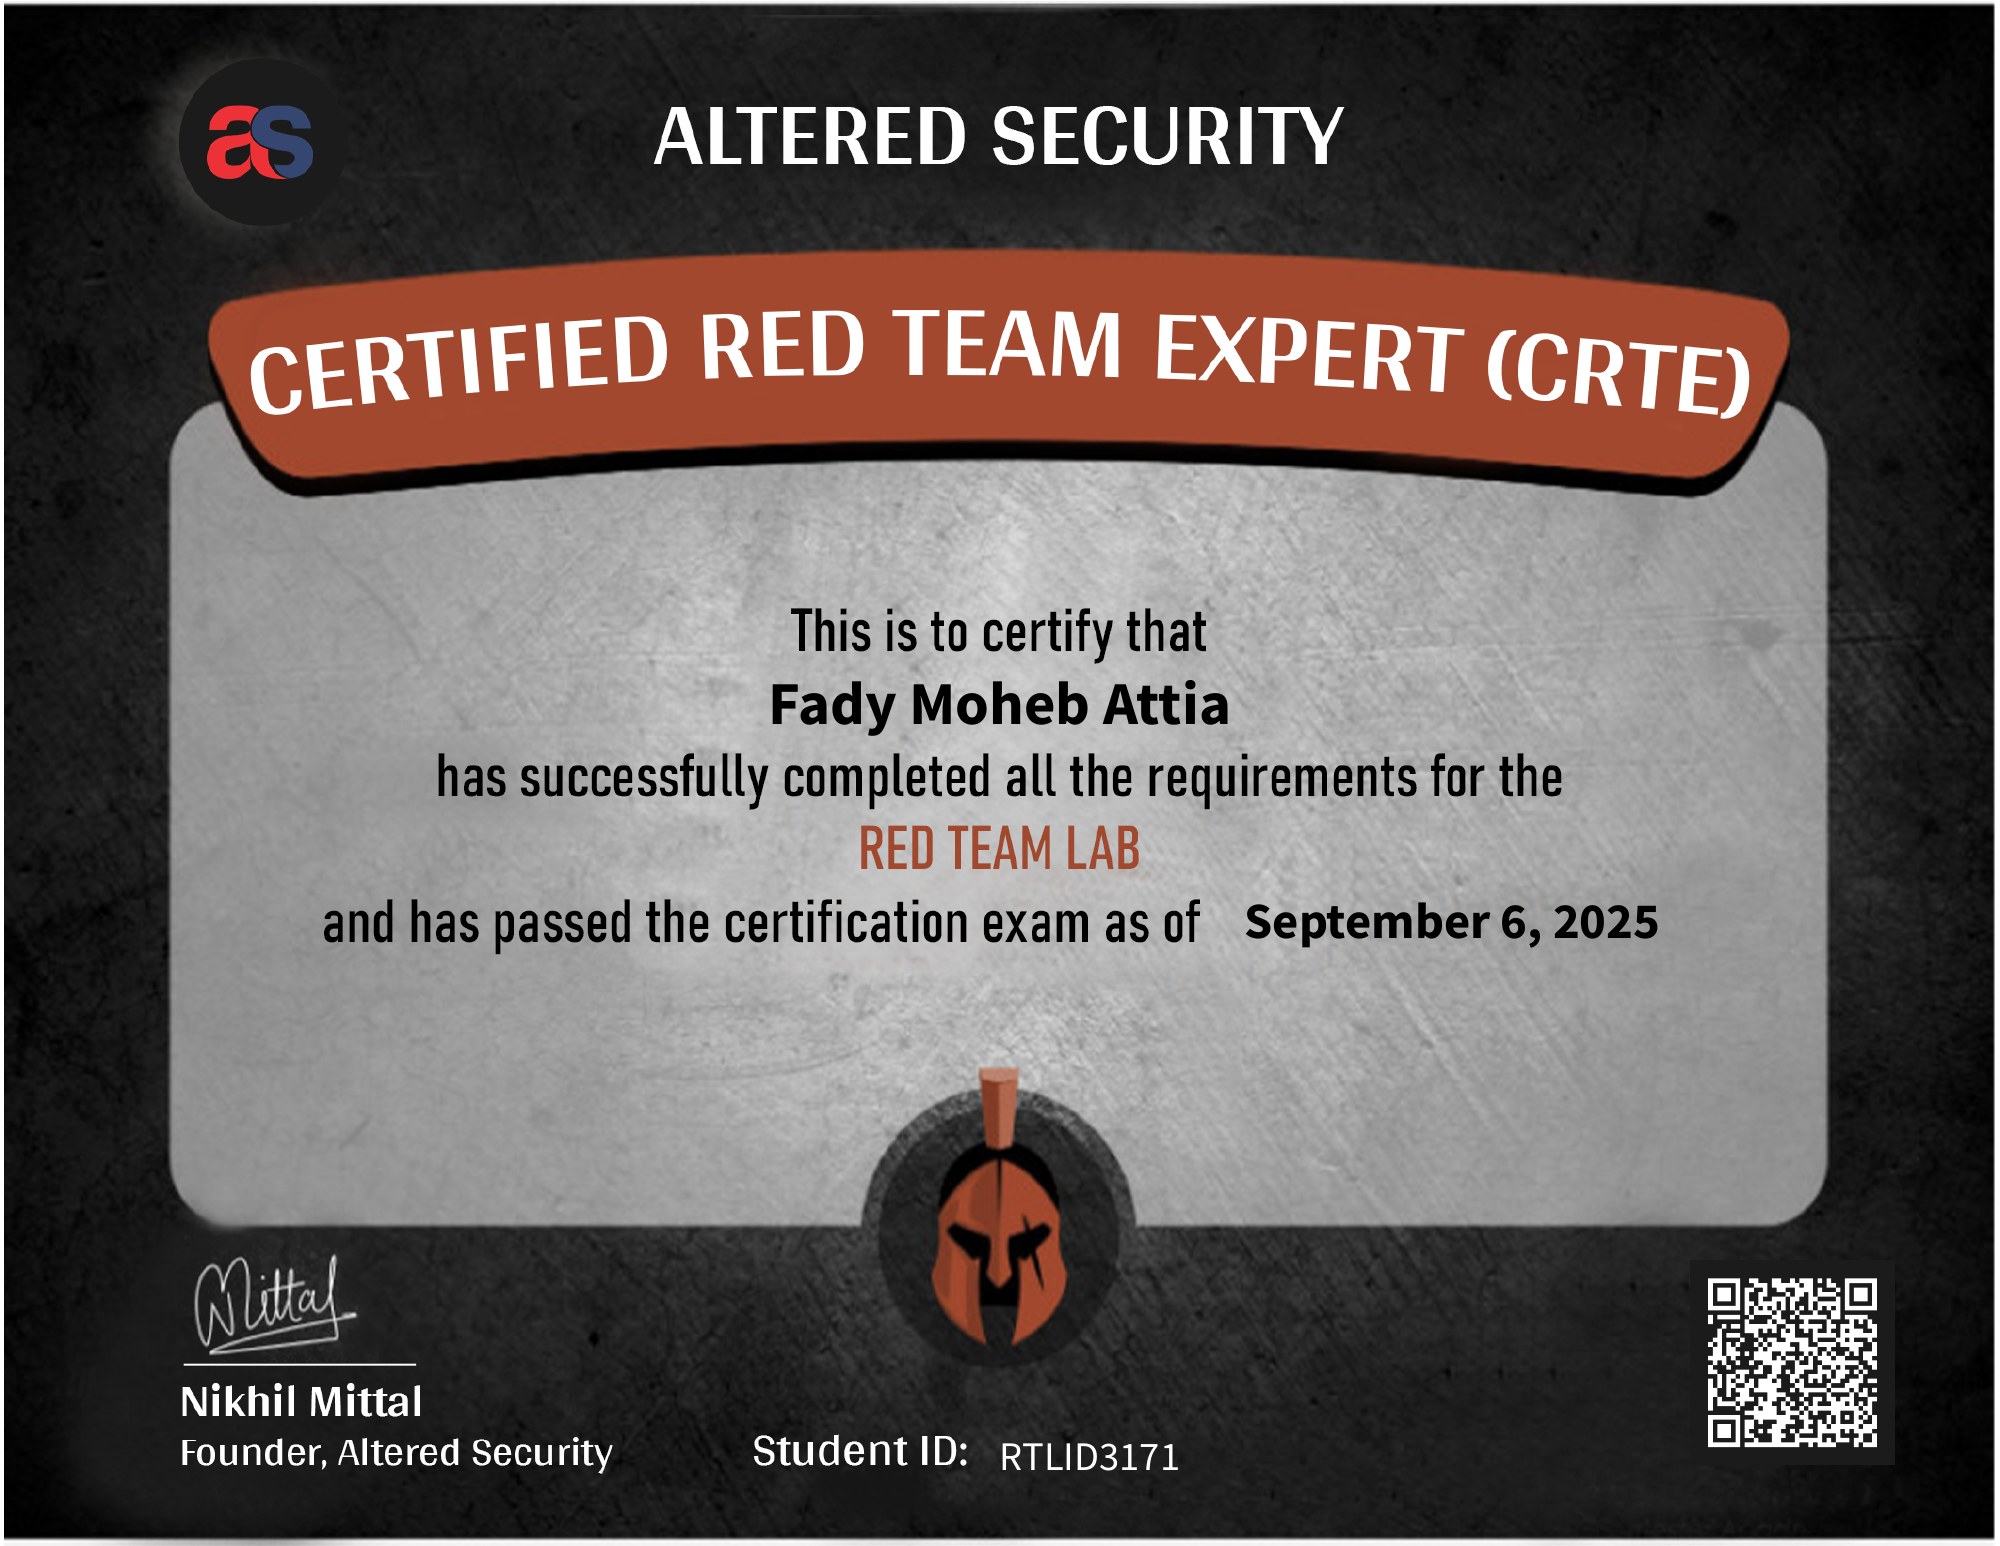
CRTECertified Red Team Expert
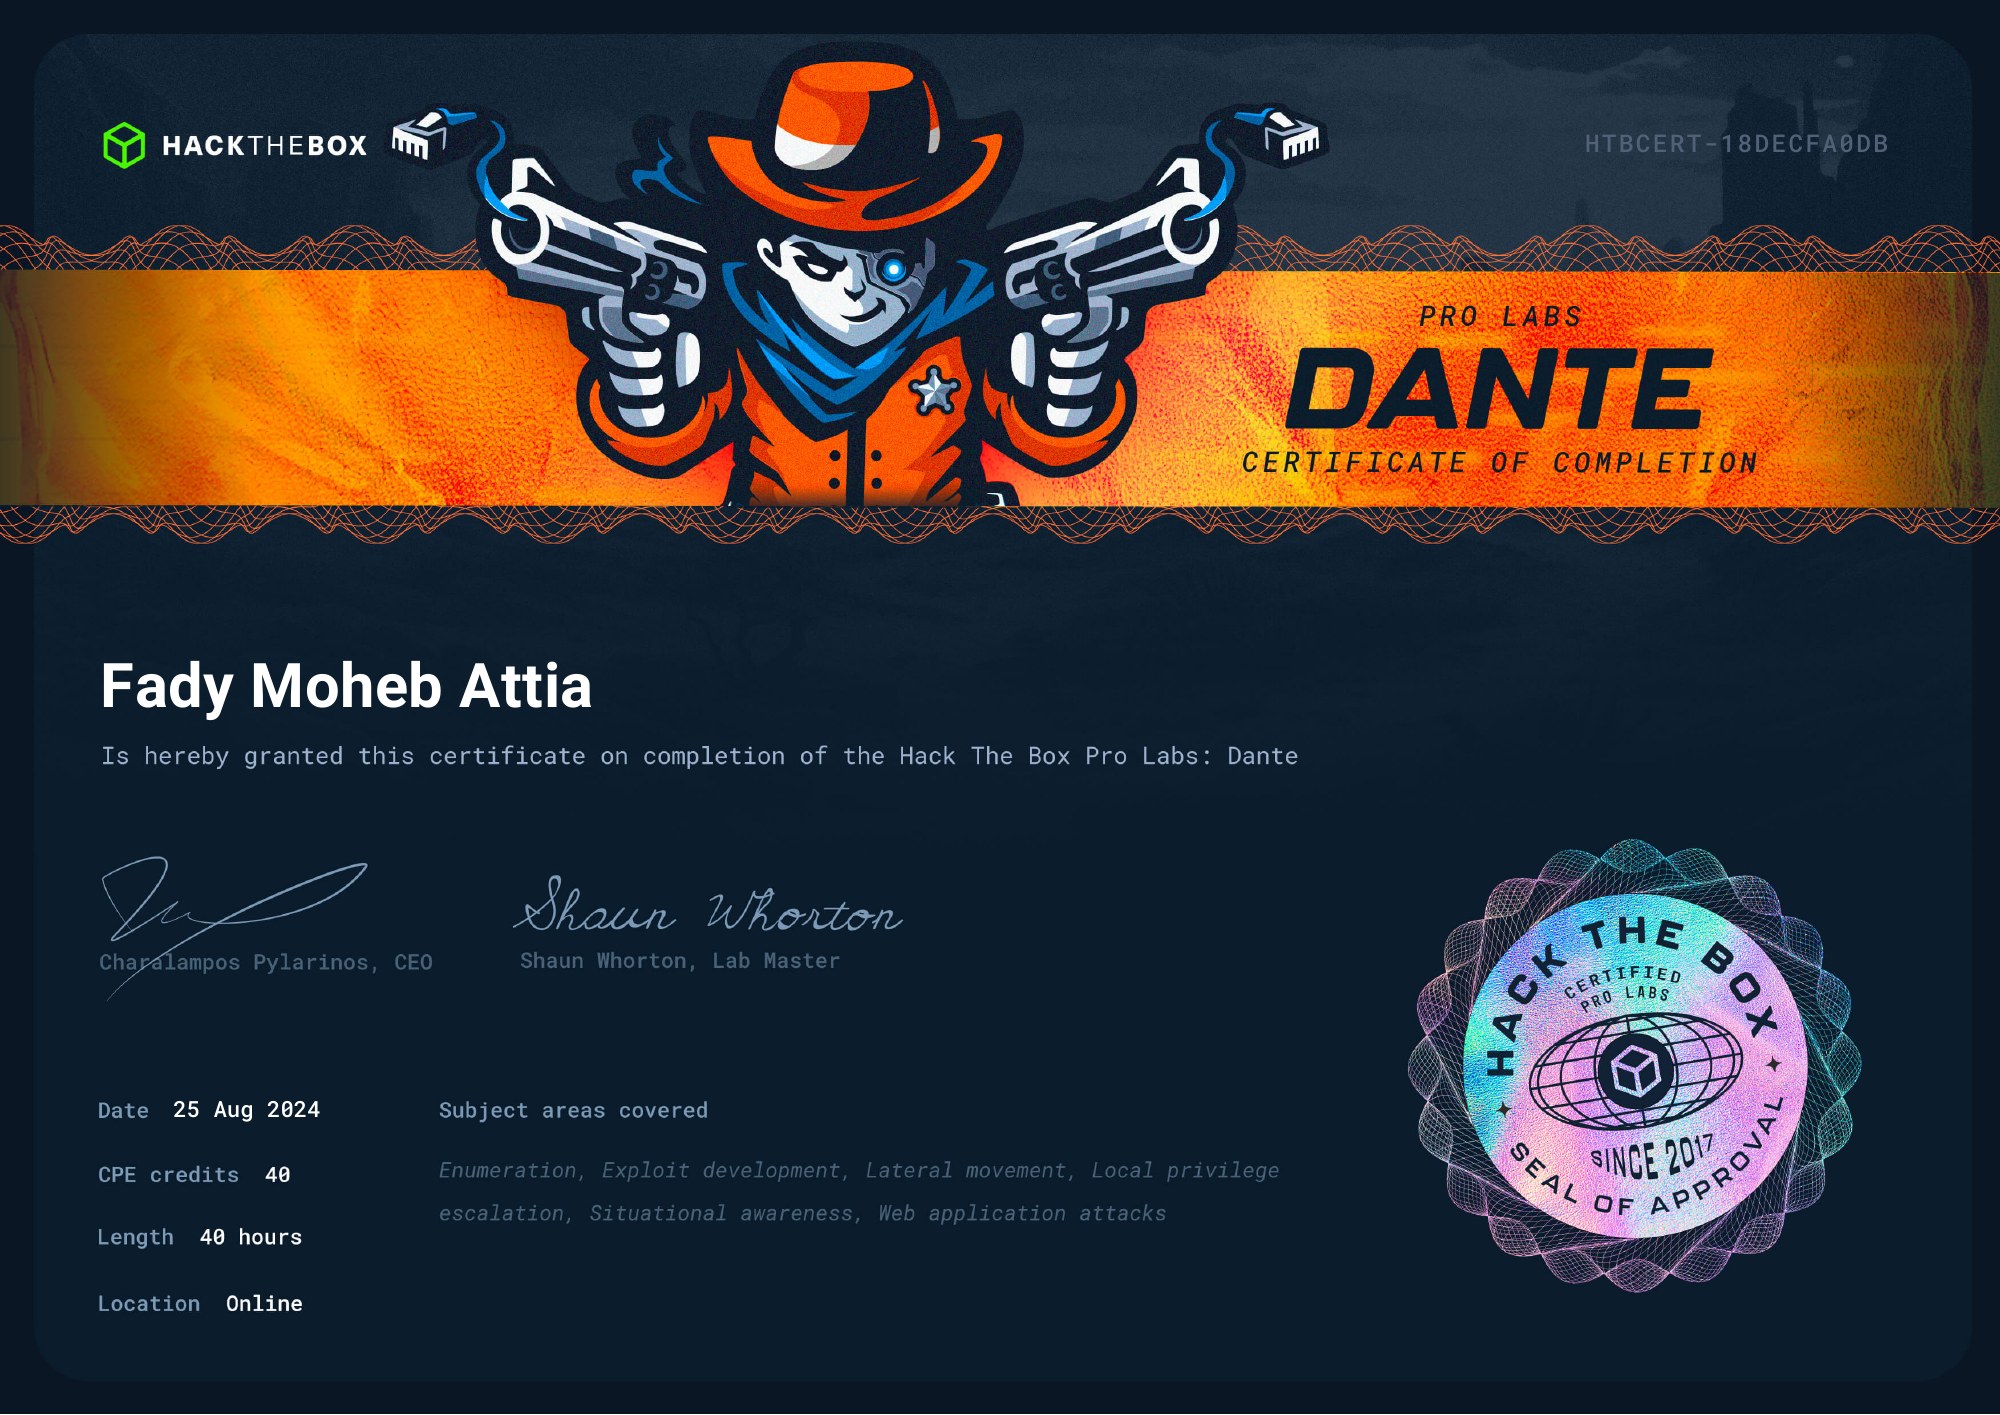
DANTEPro Labs: Dante
What I do
Read the notes (opens in a new tab)Adversary simulation end to end: initial access, Active Directory abuse, evasion against EDR and application control, and a report that shows the exact path in.
Turning what worked on the offensive side into detections that hold: telemetry, hunting queries, hardening guidance and purple-team exercises with defenders.
Tracking real actors and their tradecraft, mapping techniques to ATT&CK, and feeding that back into engagements and detections so both sides stay current.
Where the work lives
Latest
View allDuring an internal assessment, I discovered a web application called BioTime within the target infrastructure. Preliminary research uncovered multiple known vulnerabilities, specifically those listed in 2023 on CVE Details for ZKTeco, including directory traversal and limited write capabilities. Notably, a path traversal vulnerability in the iclock API of ZKTeco BioTime v8.5.5 allowed me to read arbitrary files by supplying a crafted payload.
Hey there in this article I will show you some ways that you can exploit Windows devices using Macros in a stealthy way that undetectable on windows defender , Firewall, and the user
We will deep dive into the concept of pivoting and some Redteaming stuff tips&tricks and in the end we will solve the Brainpan BOF machine
We'll cover setting up your attack lab, uncovering its hidden vulnerabilities, and crafting exploits to seize control. Learn the precise dorks to unearth countless exposed systems, turning education into a direct path to compromise.
Core Git and GitHub workflow commands for config, commits, branching, remotes, submodules, and pushing with PAT auth
Assorted Linux sysadmin fixes and one-liners for xRDP, static IPs, Tailscale routing, terminal logging, and file management
Malware development index with resources on Heaven's Gate and tools like PE-Bear, Process Hacker, and x64dbg
Collection of AI study-partner prompts for interactive red team and pentest learning in Obsidian-native output format
Dumping and decrypting SAM, SYSTEM, SECURITY and LSA secrets via reg.exe, vssadmin, Mimikatz and secretsdump.
Stay in touch
/feed.xmlEvery note and every post, one feed. Or write to [email protected] yourself.
Opens your own mail app. Nothing is stored here and there is no list.